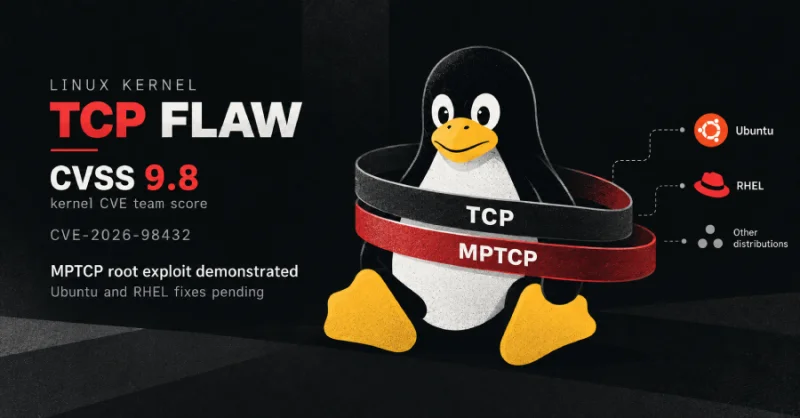
Anthropic disclosed CVE-2026-98432, a race-condition-induced use-after-free bug in Linux that can let an unauthenticated attacker execute arbitrary commands as root on servers running Multipath TCP. The exploit is zero-click, so the attacker does not need any user interaction once the target exposes an MPTCP listener.
Shweta reported that Anthropic’s proof of concept took about 53 minutes to move from the first memory leak to root-level command execution. That is the clearest sign yet that the flaw is not just theoretical; it can be driven far enough to hand over full control of a vulnerable server.
Linux kernel ownership swap
The bug sits in how Linux manages IP options during IPv4 TCP connection establishment. The kernel can pass those options from a pending connection request to a newly created socket without making a separate copy.
If another CPU is handling a retransmitted connection request at the same time, it can still use those options to build a SYNACK response. If the child socket is freed before that second CPU finishes, the kernel can read memory that no longer belongs to it.
RCU delay and fixed builds
The upstream fix defers release of the affected objects until after an RCU grace period. That changes the timing so concurrent readers are less likely to touch freed memory.
Fixed kernel packages are already available for some Debian, Oracle Linux, SUSE, and Amazon Linux releases, but Ubuntu and Red Hat Enterprise Linux had yet to release patched kernels as of October 30. The listed fixed releases are 5.10.272, 5.15.223, 6.6.159, 6.1.190, 6.12.113, 6.18.56, 7.2.10, and 7.3-rc7.
MPTCP Linux exposure
The exploit specifically targets Linux servers running an MPTCP listener. MPTCP extends conventional TCP by allowing a device to use multiple network interfaces within one connection, and Linux supports it through its networking stack.
Administrators should review kernel versions and check whether their systems expose MPTCP listeners. Mechanisms such as eBPF and other configuration techniques can also force applications to use MPTCP, so a server can be exposed even when the application did not explicitly ask for it.
The open question is which specific Linux kernel builds and distribution packages remain vulnerable right now, because the available fixed package set is not fully listed for every branch. For teams running Ubuntu and Red Hat Enterprise Linux, that missing patch status is the item to watch first.