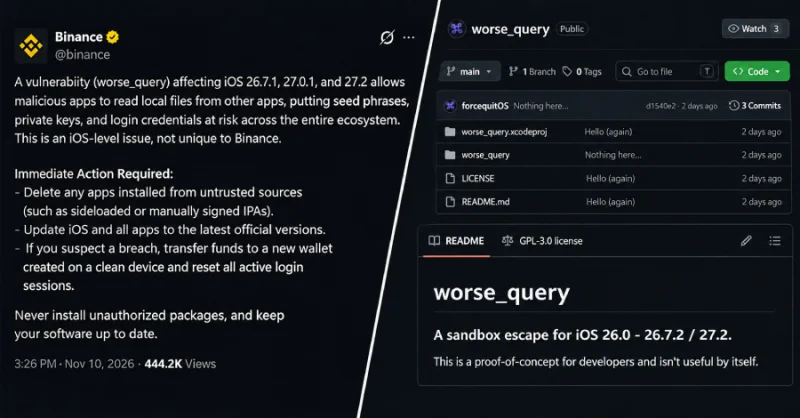
Binance warned that an iPhone hacked through a sandbox escape published on GitHub could let one app read another app’s files on iOS 26 and iOS 27. The risk reaches seed phrases, private keys, and login credentials on devices running those versions.
forcequit and worse_query
On Sunday, forcequit and 0xjohnny released the escape called worse_query, and forcequit said the code “isn't useful by itself.” The proof-of-concept can reach every app’s data container on an iPhone and some system folders on iOS 27.
To use it, an app has to set up an App Group container. That means the problem is not a broad lockpick for every app on the device.
Binance flags sideloaded apps
Binance said the practical risk centers on apps installed from untrusted sources, including sideloaded or manually signed apps. Users of those apps could expose wallet seed phrases and login credentials if a malicious app can read the same storage space.
Christoph Kolbicz built WQ Files on worse_query, and it can read other apps’ data without a jailbreak or a kernel exploit. It can also edit, delete, and clear that data, which turns the research from a demo into a tool that can be installed.
WQ Files installs through AltStore and SideStore. Those tools automatically create the App Group needed when they are used with an Apple ID.
Apple iOS 27.2.1 and iOS 26.7.3
Apple released iOS 27.2.1 and iOS 26.7.3 yesterday, but their security notes do not mention worse_query or any sandbox issue. Binance said no fix for the escape has been confirmed, and Apple says it does not disclose, discuss, or confirm security issues until it has investigated and a patch or release is available.
The mismatch leaves users with only defensive steps for now. Binance told them to delete apps from untrusted sources, update iOS and all apps, and move funds to a new wallet on a clean device if they suspect a breach.
The open question is whether an App Store app could use worse_query at all. No one involved has named a wallet app that is exposed, so the near-term task for affected users is to treat any sideloaded or manually signed app with file access as a possible entry point and rotate credentials before moving funds.