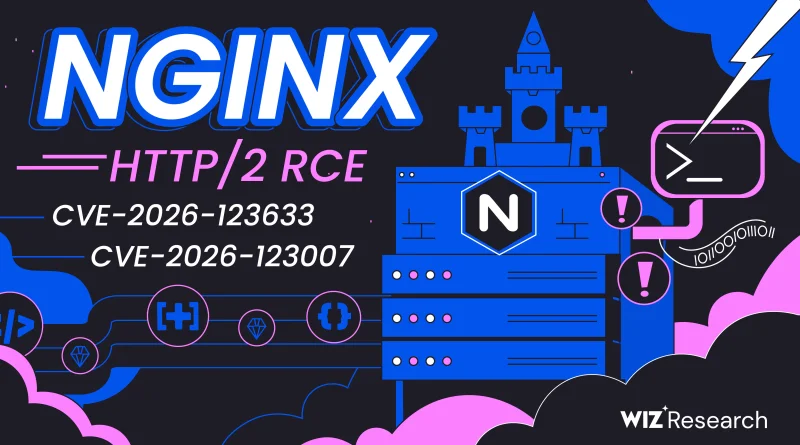
Wiz Research and four other teams found nginx2root in NGINX, where two HTTP/2 flaws tracked as CVE-2026-123633 and CVE-2026-123007 could enable unauthenticated remote code execution. The disclosure landed on November 18, 2026, so anyone running affected NGINX servers with HTTP/2 enabled now has a live remediation item, not a theoretical lab bug.
Two CVSS 4.0 9.2 flaws
Both vulnerabilities carry a CVSS 4.0 score of 9.2 and a Critical rating. That puts them in the top tier of server-side bugs because exploitation can hand an attacker control of the affected NGINX server, which then puts websites, HTTPS traffic, and API endpoints behind that server at risk.
Wiz Research used Wiz Atlas to find both flaws. It also used Gemini 4 Carbon and ChatGPT 5.6 Sol to validate their impact. The first report went to F5 on October 21, 2026, and F5 supplied a patch for that issue on November 10, 2026.
F5 release on November 18
The second report reached F5 on November 16, 2026. F5 said on November 17, 2026 that the report matched CVE-2026-123007 and would be included in the planned November 18 security release. F5 then released security updates and made a coordinated public disclosure on November 18, 2026.
That timeline matters for operators because the issue is not limited to custom application code. Wiz testing of CVE-2026-123007 showed code execution on NGINX serving ordinary static files without a backend application or third-party modules.
HTTP/2 is the trigger
The practical complication is narrow but serious. Both flaws require HTTP/2 to be enabled on the affected NGINX server, so the exposed surface depends on how the front end is configured. CVE-2026-123007 reaches back to NGINX 1.9.5 in 2015, which gives older deployments a long tail of exposure if they never tightened their HTTP/2 handling.
NGINX often sits in front of several applications at once, so one vulnerable deployment can affect more than one website or API. The next step for administrators is to identify every NGINX instance with HTTP/2 enabled and apply the security updates once they are available in their environment.
The unanswered question is the exact version and deployment scope for each flaw across every affected NGINX build. Until that list is pinned down, the safest assumption is that any HTTP/2-enabled NGINX front end deserves immediate review.